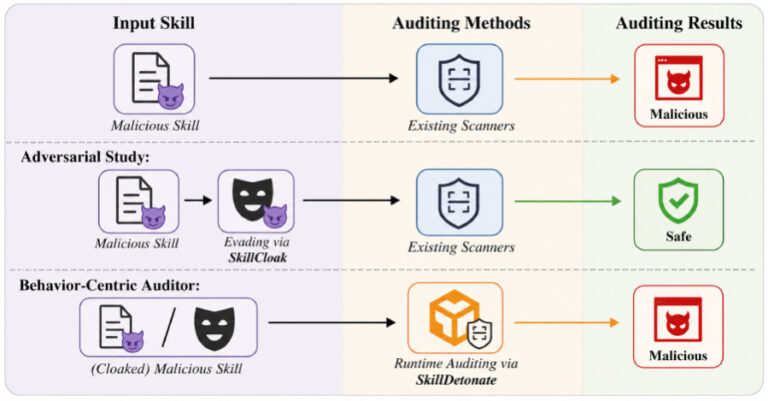
SkillCloak Lets Malicious AI Agent Skills Evade Static Scanners with Self-Extracting Packing
Scanners meant to catch malicious add-on “skills” for AI coding agents can be fooled by a few simple changes that leave the malware working, according
Scanners meant to catch malicious add-on “skills” for AI coding agents can be fooled by a few simple changes that leave the malware working, according
Researchers found a flaw in Opera GX, the gaming-focused version of the Opera browser, that let a malicious website silently install a browser add-on and use

A U.S. government entity paid about $1 million to keep stolen files from being leaked, according to a new case study by Rakesh Krishnan for Ransom-ISAC,

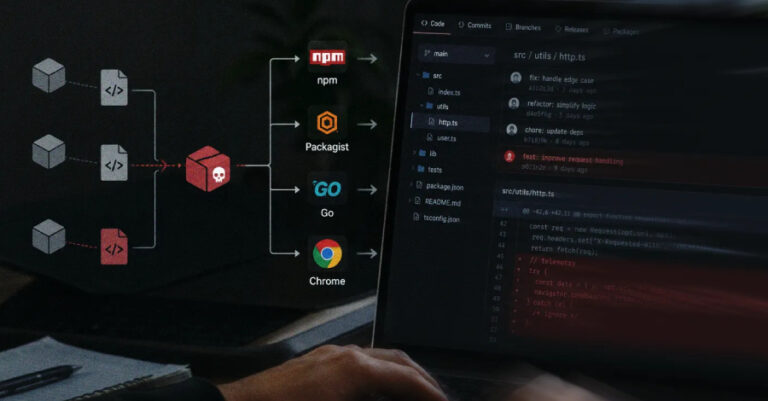
The North Korean threat actors linked to the Contagious Interview campaign have been observed publishing 108 unique packages and web browser extensions spanning npm, Packagist,

A newly disclosed Linux kernel flaw called Bad Epoll (CVE-2026-46242) lets an ordinary user with no special access take full control of a machine as

Security firm runZero has disclosed seven vulnerabilities in FatFs, a small filesystem library that lets a device read and write the FAT and exFAT formats used on USB

Cybersecurity researchers have discovered a previously undocumented modular malware framework codenamed Avalon that’s distributed by means of a multi-stage phishing chain capable of bypassing traditional

Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade as Rollup polyfill tooling to

A previously undocumented threat actor known as Armored Likho has been attributed to cyber attacks targeting government agencies and the electric power sector across Russia,

A new report from the Citizen Lab has revealed that former Member of the European Parliament Stelios Kouloglou had his mobile device repeatedly hacked with