CERT/CC Warns of Hidden Admin Backdoor in Tenda Router Firmware
Several versions of firmware released by Chinese network device manufacturer Tenda have been found to embed an undocumented authentication backdoor that enables administrative access to

Several versions of firmware released by Chinese network device manufacturer Tenda have been found to embed an undocumented authentication backdoor that enables administrative access to

BeyondTrust has released updates to address two critical security flaws affecting Remote Support (RS) and Privileged Remote Access (PRA) products that, if successfully exploited, could

An Iranian hacking group affiliated with Iran’s Ministry of Intelligence and Security (MOIS) has been wielding a previously undocumented modular command-and-control (C2) framework dubbed Cavern

A use-after-free bug in Linux’s KVM hypervisor can be triggered from a guest virtual machine to corrupt the shadow-page state of the host kernel that

Threat actors have been observed attempting to exploit a recently patched critical security flaw in Gitea Docker images, according to Sysdig. The vulnerability in question

A suspected China-nexus threat activity cluster has been observed targeting Indian taxpayers, tax professionals, and corporate finance teams to deliver a remote access trojan designed

Building a shortlist for an AI SOC evaluation can be tough. SIEM, SOAR, and pureplay AI SOC vendors are all saying the same thing. But

A streaming box should not need a threat model. Neither should a username field, a demo repo, a reset flow, or a browser permission prompt.

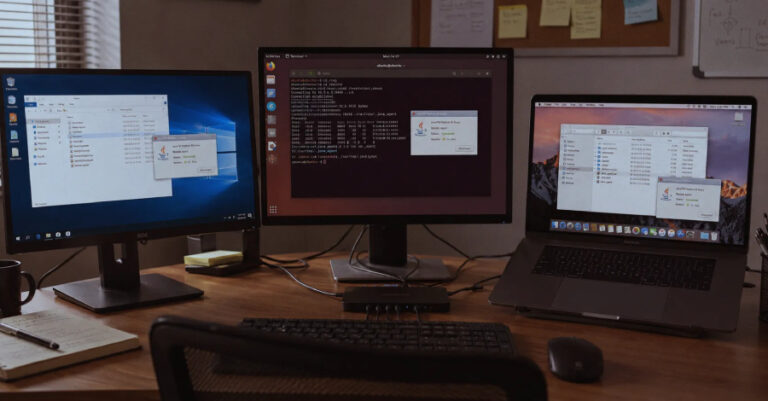
Cybersecurity researchers have flagged a novel Java-based remote access trojan (RAT) called QuimaRAT that’s capable of targeting Windows, Linux, and macOS environments. According to LevelBlue,

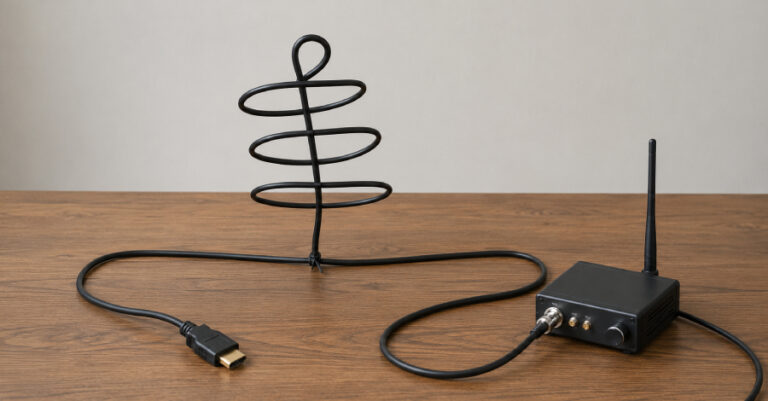
Researchers at Shandong University have shown a fast new way to pull data off computers that are cut off from every network. The technique, called TrojPix, tweaks on-screen