Hacker Runs Hermes AI Agent Unattended for Post-Exploitation at Thai Finance Ministry
Someone installed a popular AI assistant on a rented server, switched off the setting that makes it ask permission before running risky commands, and pointed
Someone installed a popular AI assistant on a rented server, switched off the setting that makes it ask permission before running risky commands, and pointed
Redis shipped seven security releases on July 23 after researchers published authenticated RCE PoCs for stock Redis 6.2.22, 7.4.9, 8.6.4, and 8.8.0. All four chains

Eight security flaws in NodeBB went public on Wednesday, along with the code to exploit them. Aikido Security rates all eight as high severity and

The Computer Emergency Response Team of Ukraine (CERT-UA) has warned of a new campaign that involves the use of a malicious program that’s dressed up

A Russian state-supported espionage group spent months reading Western mailboxes through a then-unknown flaw in Zimbra’s webmail client. The payload goes after the last 90

Most of this week’s trouble came dressed as something useful. A package stole data. A fake extension opened remote access. A safety app became spyware.

An exposed Alibaba Cloud server has revealed a China-nexus operation that Group-IB tracks as JadeProx. The cluster has targeted government, healthcare, and education organizations across

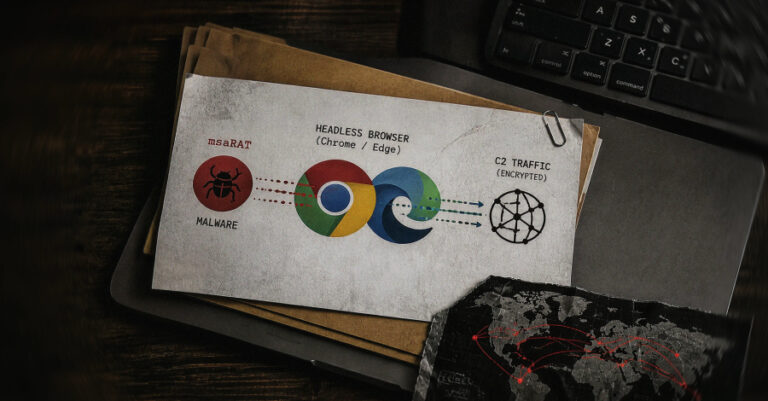
The Chaos ransomware group ran its command-and-control through the victim’s own browser. Cisco Talos on Thursday detailed msaRAT, the Rust implant behind it, found on

Cybersecurity researchers have uncovered a sandbox escape vulnerability in Anthropic’s Claude Cowork that makes it possible to break out of the confines of a Linux

Google on Thursday announced a new way for users to sign-in to their accounts by letting them take a selfie video. The selfie for sign-in,