Industry News
18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers
A use-after-free bug in Linux’s SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to

A use-after-free bug in Linux’s SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to
Open Source had a great childhood. For two decades it got to be a kid. It ran around barefoot, gave everything away, trusted strangers, and
A GitHub issue opened by an account with no repository privileges was enough to execute code on the CI runners behind Anthropic’s and Google’s own
Entra ID researcher Dirk-jan Mollema demonstrated that malware already running in a signed-in Windows session can silently use the victim’s Windows Hello for Business key
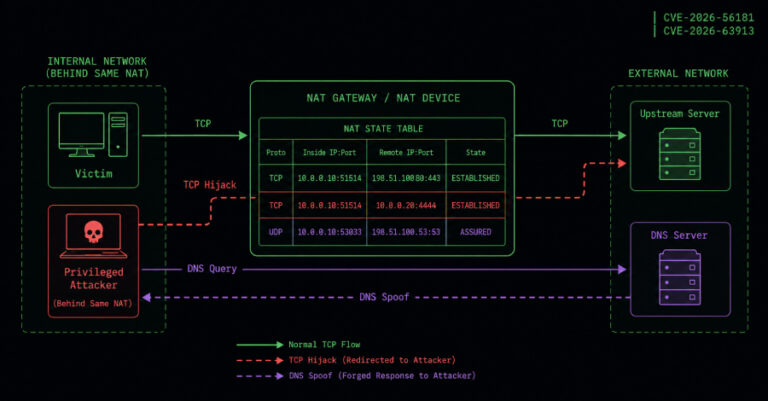
Security researcher Malcolm Stagg has disclosed a new attack class called NatJack that manipulates network address translation (NAT) connection state to hijack active TCP sessions, spoof DNS
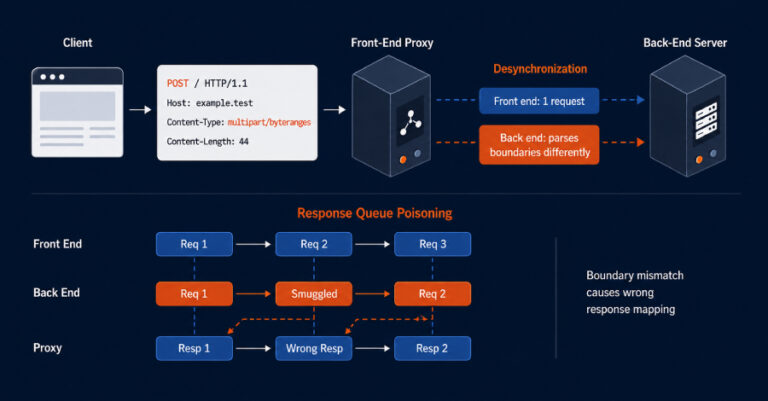
PortSwigger says HTTP Terminator, an artificial intelligence (AI)-assisted research system built by James Kettle, generated and proved new HTTP desynchronization techniques after exploring 30,000 candidate
Cybersecurity researchers have called attention to an active “widespread email-driven phishing campaign” that employs adversary-in-the-middle (AitM) techniques to take control of Microsoft 365 accounts with
A new analysis has uncovered that the threat actor tracked as TeamPCP has been active on the cybercrime scene as far back as 2020, indicating
Cisco has rolled out updates to address multiple critical security vulnerabilities impacting Catalyst SD-WAN and IOS XE Software as part of a comprehensive internal security
Zapscape, a new Linux kernel vulnerability, could allow an attacker with kernel privileges inside an L1 guest virtual machine (VM) to escape KVM isolation and