Amazon Q Developer Flaw Could Let Malicious Repos Run Code via MCP Configs
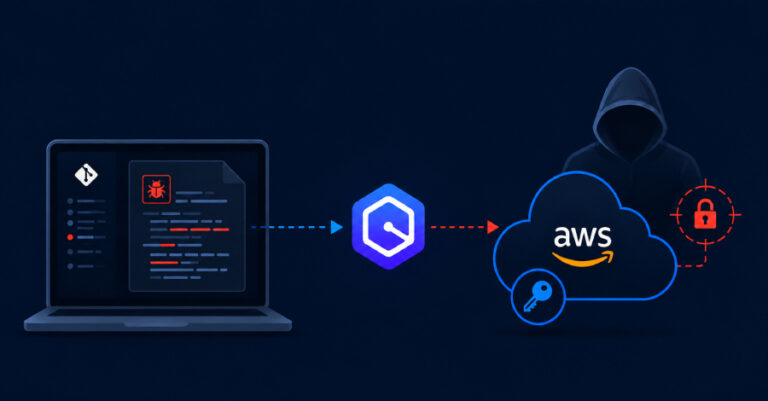
A high-severity flaw in Amazon Q Developer let a malicious repository run commands and steal a developer’s cloud credentials. The path was short: a developer
A high-severity flaw in Amazon Q Developer let a malicious repository run commands and steal a developer’s cloud credentials. The path was short: a developer
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a critical remote code execution vulnerability impacting PTC Windchill PDMlink and PTC FlexPLM enterprise

A flaw in the Linux kernel’s traffic-control subsystem can let a local unprivileged user gain root on affected systems. CVE-2026-46331, nicknamed “pedit COW,” is an

Cybersecurity researchers have flagged yet another evolution of the supply chain attack linked to the Mini Shai-Hulud, Miasma, and Hades malware family that has compromised

AI agents are moving through enterprise environments, inheriting permissions, traversing systems, and executing decisions at machine speed with minimal oversight. The identity infrastructure built to

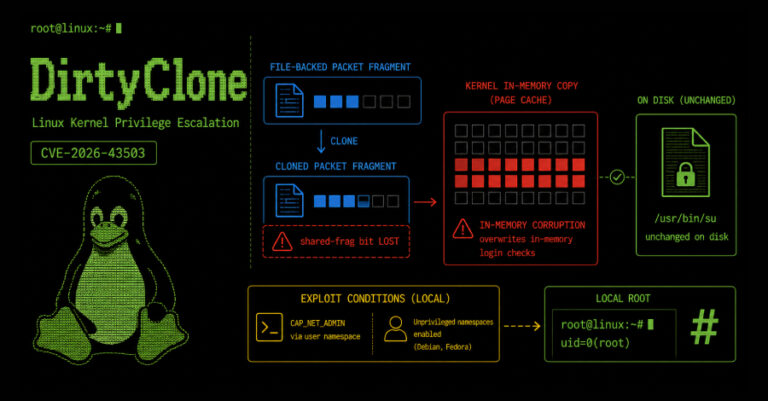
DirtyClone is a new Linux kernel privilege escalation in the DirtyFrag family. JFrog Security Research published a working exploit walkthrough for the flaw on June 25, the

An active phishing campaign has been targeting hotel and other hospitality organizations across Europe and Asia since April 2026, using photo-themed ZIP files to drop

The Russian state-sponsored threat actor known as Turla has been attributed to a previously undocumented .NET backdoor called STOCKSTAY that has been deployed against government

Russian authorities used Cellebrite’s UFED forensic tools to break into the iPhone of detained opposition activist Andrey Pivovarov in June 2021, three months after Cellebrite

An analysis of a popular Google Chrome ad block extension for YouTube has uncovered the ability to execute arbitrary JavaScript code. According to Island, the