Unpatched Flaws Disclosed in Filesystem Bundled Into Millions of Embedded Devices
Security firm runZero has disclosed seven vulnerabilities in FatFs, a small filesystem library that lets a device read and write the FAT and exFAT formats used on USB
Security firm runZero has disclosed seven vulnerabilities in FatFs, a small filesystem library that lets a device read and write the FAT and exFAT formats used on USB
Cybersecurity researchers have discovered a previously undocumented modular malware framework codenamed Avalon that’s distributed by means of a multi-stage phishing chain capable of bypassing traditional

Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade as Rollup polyfill tooling to

A previously undocumented threat actor known as Armored Likho has been attributed to cyber attacks targeting government agencies and the electric power sector across Russia,

A new report from the Citizen Lab has revealed that former Member of the European Parliament Stelios Kouloglou had his mobile device repeatedly hacked with

Cybersecurity researchers have flagged a new macOS information stealer called PamStealer that employs a series of clever tricks to infect systems and siphon sensitive data.

Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. “Although tactics differ

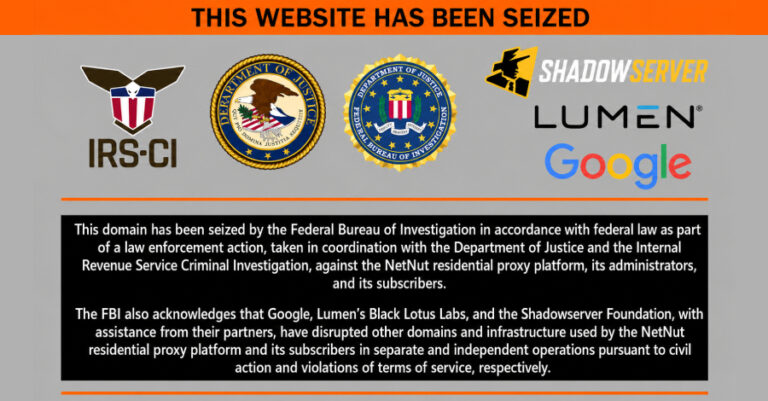
Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people’s traffic. Working with the FBI,

This week’s security news is mostly about weak spots. Browsers, bots, sandboxes, AI systems, and email flows all show the same problem in different ways.

The threat actor known as ToddyCat has been attributed to a new malware called Umbrij that’s designed to gain surreptitious access to a victim’s email