Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point’s Security Management and Log Servers could allow an attacker without login credentials to run code as root on those
A critical vulnerability in Check Point’s Security Management and Log Servers could allow an attacker without login credentials to run code as root on those
OpenAI on Wednesday disclosed six new instances of “unexpected or concerning model behavior” that took place over the past six months, while sharing a new

The China-aligned state-sponsored threat actor known as FamousSparrow has been observed deploying a previously unreported backdoor called SparroWocky in attacks targeting multiple countries in Latin

Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR

A new CVE drops. Your scanner finds it. The severity score looks ugly. But that still does not answer the question that matters: Can it

Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday.

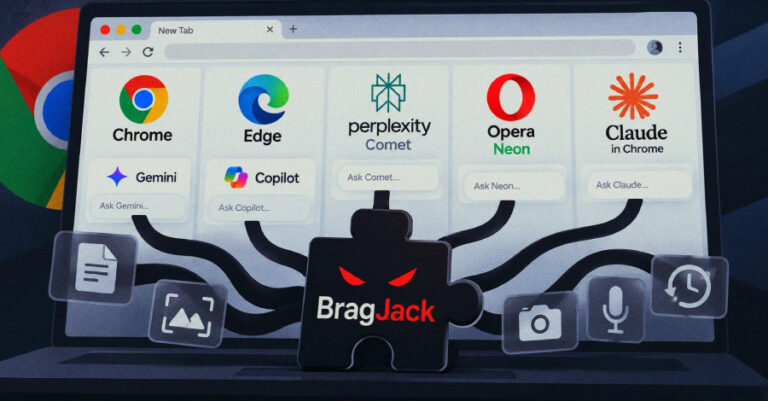
Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in

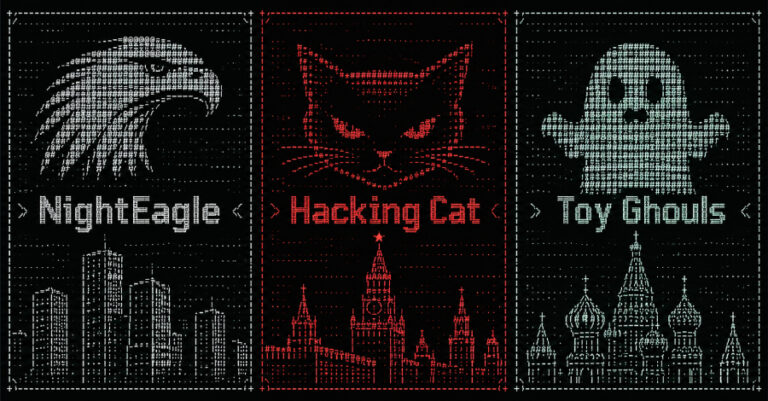
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports

A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability in

Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac,