Industry News
How to Close Threat Detection Gaps: Your SOC’s Action Plan
Running a SOC often feels like drowning in alerts. Every morning, dashboards light up with thousands of signals; some urgent, many irrelevant. The job is

Running a SOC often feels like drowning in alerts. Every morning, dashboards light up with thousands of signals; some urgent, many irrelevant. The job is
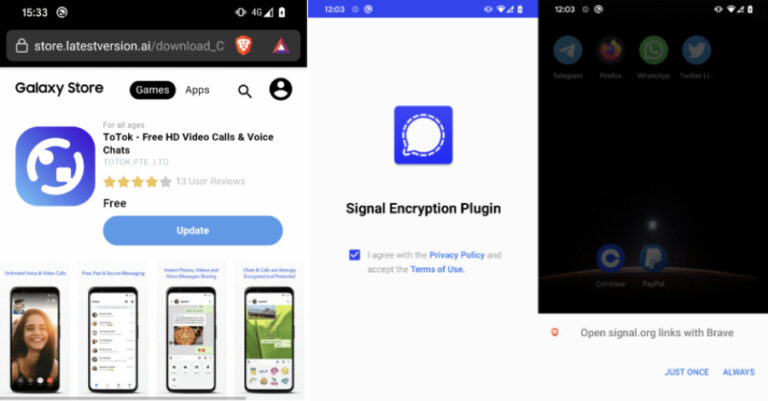
Cybersecurity researchers have discovered two Android spyware campaigns dubbed ProSpy and ToSpy that impersonate apps like Signal and ToTok to target users in the United
In yet another piece of research, academics from Georgia Institute of Technology and Purdue University have demonstrated that the security guarantees offered by Intel’s Software
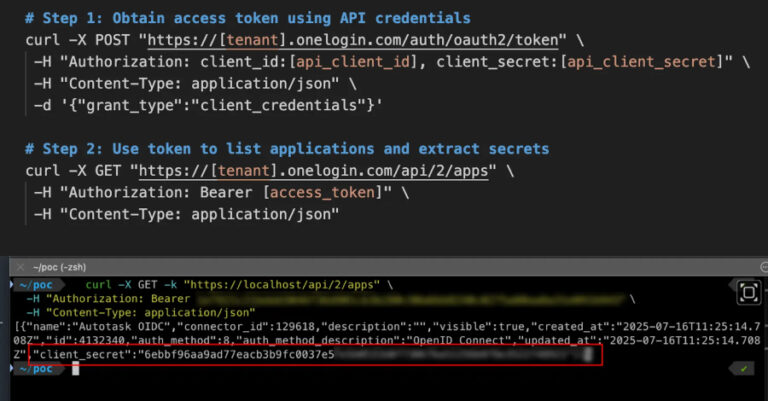
A high-severity security flaw has been disclosed in the One Identity OneLogin Identity and Access Management (IAM) solution that, if successfully exploited, could expose sensitive
A severe security flaw has been disclosed in the Red Hat OpenShift AI service that could allow attackers to escalate privileges and take control of
AI is changing automation—but not always for the better. That’s why we’re hosting a new webinar, “Workflow Clarity: Where AI Fits in Modern Automation,” with
Unknown threat actors are abusing Milesight industrial cellular routers to send SMS messages as part of a smishing campaign targeting users in European countries since
Bitdefender’s 2025 Cybersecurity Assessment Report paints a sobering picture of today’s cyber defense landscape: mounting pressure to remain silent after breaches, a gap between leadership
A previously undocumented Android banking trojan called Klopatra has compromised over 3,000 devices, with a majority of the infections reported in Spain and Italy. Italian
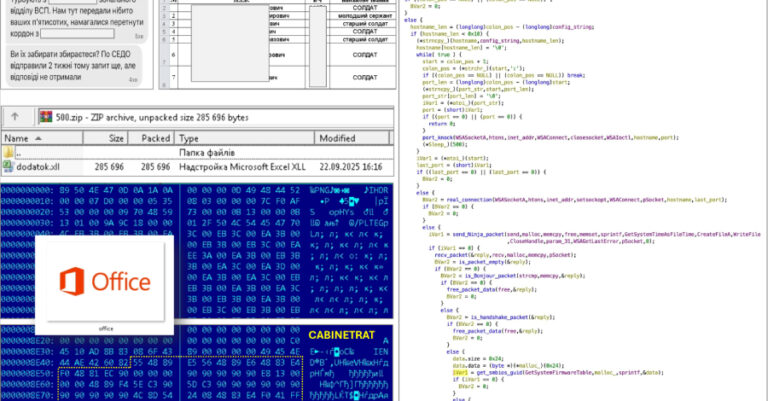
The Computer Emergency Response Team of Ukraine (CERT-UA) has warned of new targeted cyber attacks in the country using a backdoor called CABINETRAT. The activity,