Poisoned Ruby Gems and Go Modules Exploit CI Pipelines for Credential Theft
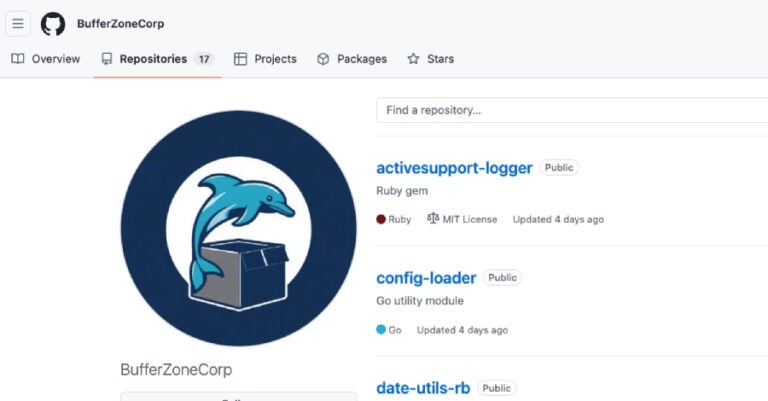
A new software supply chain attack campaign has been observed using sleeper packages as a conduit to subsequently push malicious payloads that enabled credential theft,
A new software supply chain attack campaign has been observed using sleeper packages as a conduit to subsequently push malicious payloads that enabled credential theft,
In yet another software supply chain attack, threat actors have managed to compromise the popular Python package Lightning to push two malicious versions to conduct

The internet is noisy this week. We are seeing some wild new tactics, like people using fake cell towers to send scam texts, while some

Intro A sophisticated, high-resilience malicious campaign was identified by Atos Threat Research Center (TRC) in March 2026. This operation specifically targets the high-privilege professional accounts

Cybersecurity researchers have disclosed details of a stealthy Python-based backdoor framework called DEEP#DOOR that comes with capabilities to establish persistent access and harvest a wide

Cybersecurity researchers have disclosed details of a Linux local privilege escalation (LPE) flaw that could allow an unprivileged local user to obtain root. The high-severity

Google has addressed a maximum severity security flaw in Gemini CLI — the “@google/gemini-cli” npm package and the “google-github-actions/run-gemini-cli” GitHub Actions workflow — that could

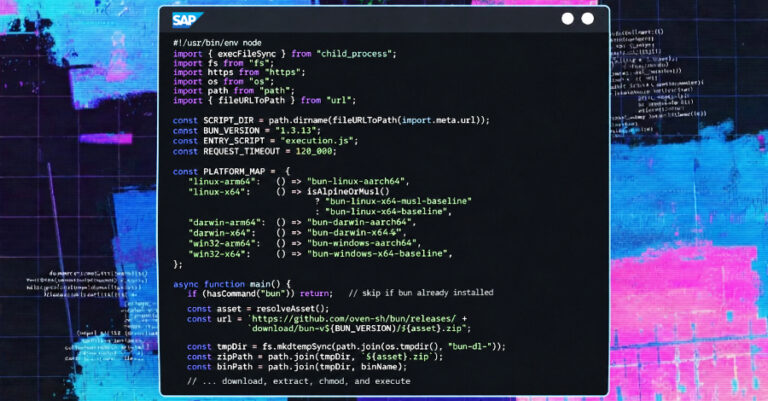
Cybersecurity researchers are sounding the alarm about a new supply chain attack campaign targeting SAP-related npm Packages with credential-stealing malware. According to reports from Aikido

Cybersecurity researchers have discovered malicious code in an npm package after a malicious package as a dependency to the project by Anthropic’s Claude Opus large

In February 2026, researchers uncovered a shift that completely changed the game: threat actors are now using custom AI setups to automate attacks directly into