Google DoubleClick Abused in New Malspam Campaign to Deliver DesckVB RAT
Cybersecurity researchers have flagged a new malspam campaign that makes use of Google’s DoubleClick domain as a way to evade detection and ultimately deliver a
Cybersecurity researchers have flagged a new malspam campaign that makes use of Google’s DoubleClick domain as a way to evade detection and ultimately deliver a
A single poisoned notification from WhatsApp, Slack, SMS, Signal, Instagram, or Messenger could have hijacked Google Gemini’s voice assistant on Android and made it open

Assume the breach. Zero-days keep shipping, AI is writing exploits faster than anyone patches, and “patch everything in time” stopped working years ago. Stop betting

The Fragmented State of Modern Enterprise Identity Enterprise IAM is approaching a breaking point. As organizations scale, identity becomes increasingly fragmented across thousands of applications,

Cybersecurity researchers have disclosed a one-click attack via Microsoft Visual Studio Code (VS Code) that makes it possible to steal a user’s GitHub token. “Just

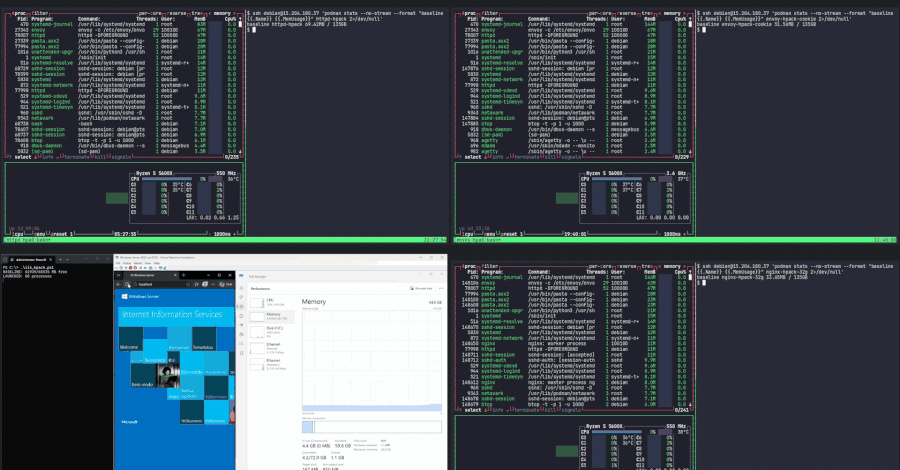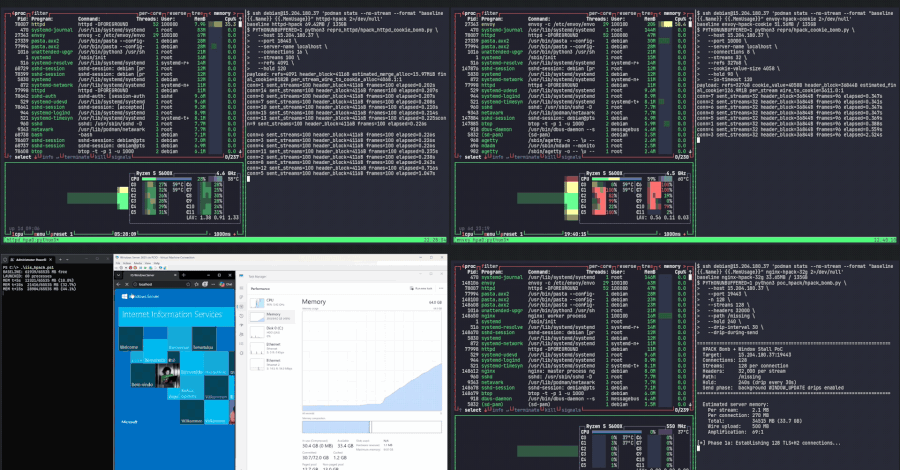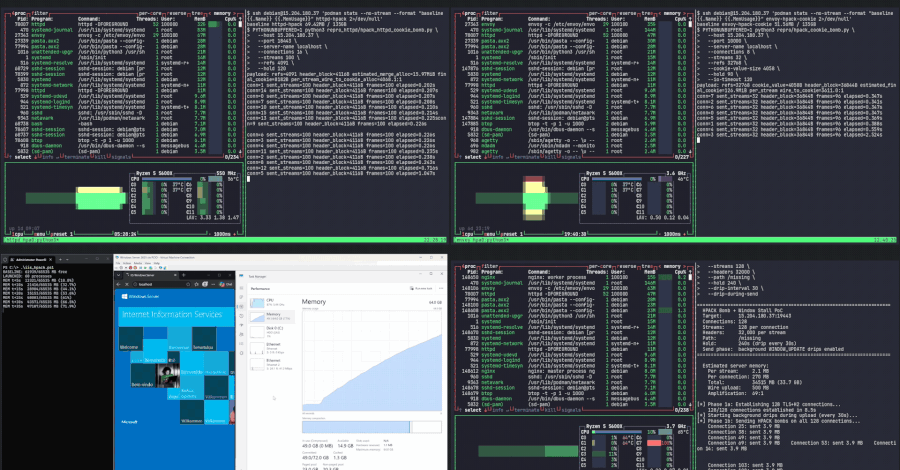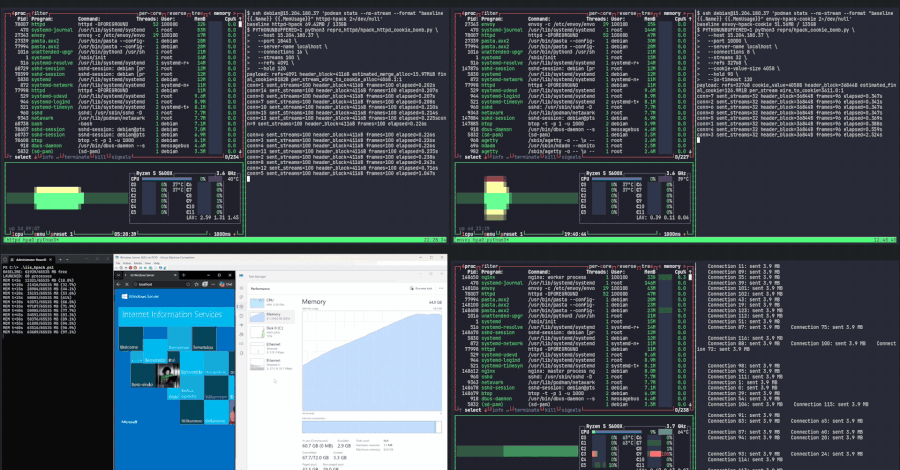
Cybersecurity researchers have discovered a remote denial-of-service exploit that affects major web servers, including NGINX, Apache HTTPD, Microsoft IIS, Envoy, and Cloudflare Pingora. The vulnerability

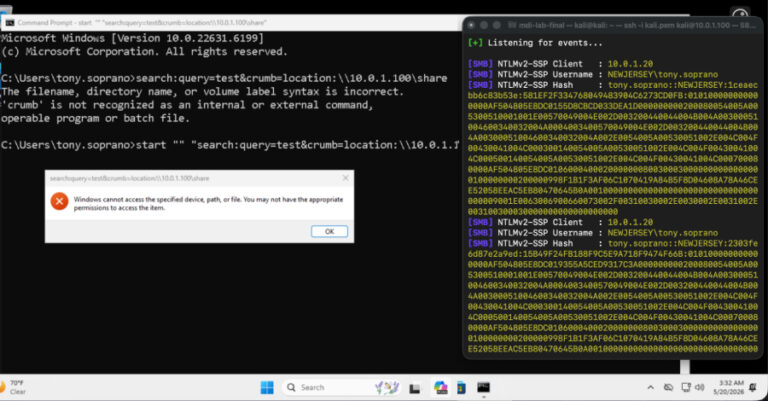
Cybersecurity researchers have disclosed details of an unpatched issue that could be exploited to disclose a user’s NTLMv2 hash to the attacker. Like in the

Cybersecurity researchers have flagged a new campaign targeting Minecraft players via YouTube to spread malware capable of gaining control of victims’ systems. The Minecraft-focused malware-as-a-service

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a high-severity security flaw impacting Oracle WebLogic Server to its Known Exploited Vulnerabilities (KEV)

The Russian hacking group known as Gamaredon has been attributed to the continued exploitation of a WinRAR vulnerability to deliver multiple malware families aimed at