Industry News
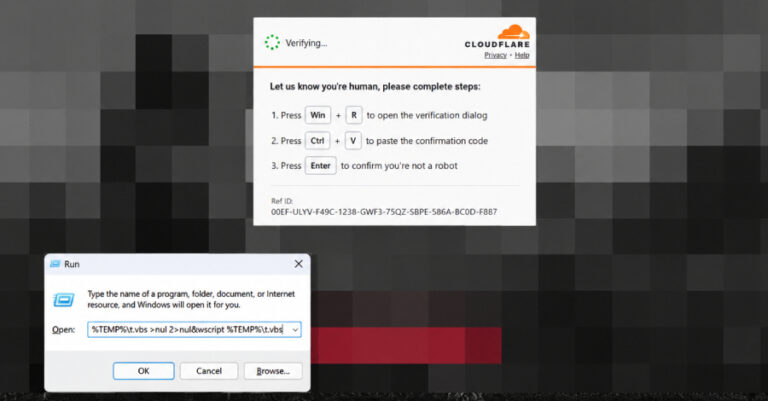
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of
A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem.
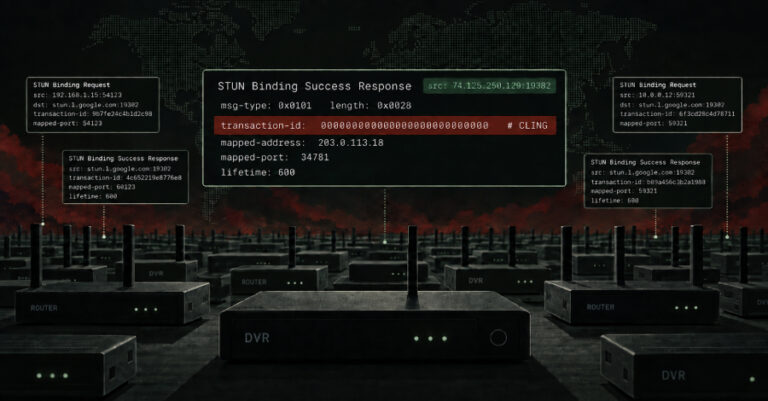
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps
Apple has announced that it’s taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS