One Missed Threat Per Week: What 25M Alerts Reveal About Low-Severity Risk
The dark secret of enterprise security operations is that defenders have quietly institutionalized the practice of not looking. This is not just anecdotal, but rather
The dark secret of enterprise security operations is that defenders have quietly institutionalized the practice of not looking. This is not just anecdotal, but rather
A previously undocumented Linux implant codenamed Quasar Linux RAT (QLNX) is targeting developers’ systems to establish a silent foothold as well as facilitate a broad

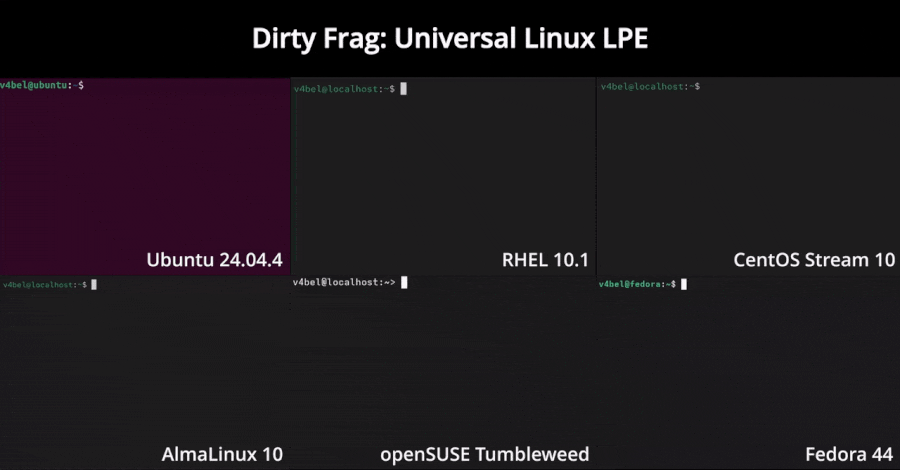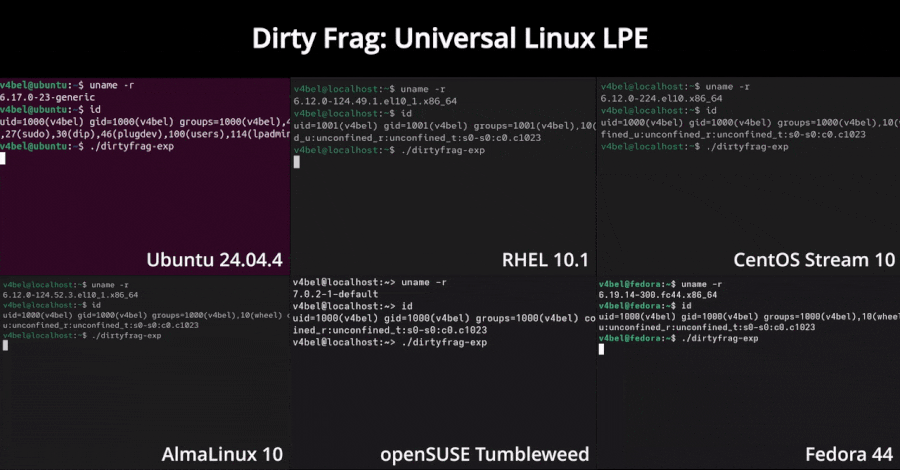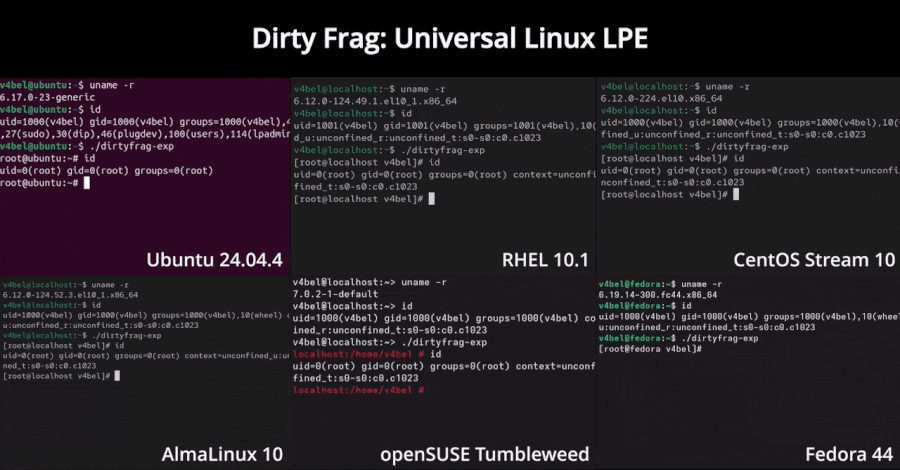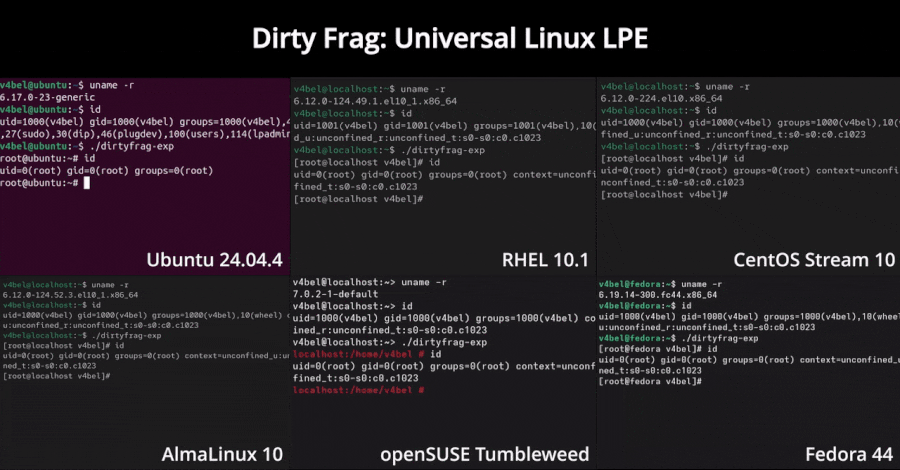
Details have emerged about a new, unpatched local privilege escalation (LPE) vulnerability impacting the Linux kernel. Dubbed Dirty Frag, it has been described as a

Cybersecurity researchers have disclosed details of a new credential theft framework dubbed PCPJack that targets exposed cloud infrastructure and ousts any artifacts linked to TeamPCP

Ivanti is warning that a new security flaw impacting Endpoint Manager Mobile (EPMM) has been explored in limited attacks in the wild. The high-severity vulnerability,

The hardest part of cybersecurity isn’t the technology, it’s the people. Every major breach you’ve read about lately usually starts the same way: one employee,

Palo Alto Networks has disclosed that threat actors may have attempted to unsuccessfully exploit a recently disclosed critical security flaw as early as April 9,

Having an incident response retainer, or even a pre-approved external incident response firm, is not the same as being ready for an incident. A retainer

Bad week. Turns out the easiest way to get hacked in 2026 is still the same old garbage: shady packages, fake apps, forgotten DNS junk,

Cybersecurity researchers have discovered three packages on the Python Package Index (PyPI) repository that are designed to stealthily deliver a previously unknown malware family called ZiChatBot