cPanel CVE-2026-41940 Under Active Exploitation to Deploy Filemanager Backdoor
A threat actor named Mr_Rot13 has been attributed to the exploitation of a recently disclosed critical cPanel flaw to deploy a backdoor codenamed Filemanager on

A threat actor named Mr_Rot13 has been attributed to the exploitation of a recently disclosed critical cPanel flaw to deploy a backdoor codenamed Filemanager on
Google on Monday disclosed that it identified an unknown threat actor using a zero-day exploit that it said was likely developed with an artificial intelligence

Rough Monday. Somebody poisoned a trusted download again, somebody else turned cloud servers into public housing, and a few crews are still getting into boxes

Defending a network at 2 am looks a lot like this: an analyst copy-pasting a hash from a PDF into a SIEM query. A red

A malicious Hugging Face repository managed to take a spot in the platform’s trending list by impersonating OpenAI’s Privacy Filter open-weight model to deliver a

Cybersecurity researchers have disclosed a critical security vulnerability in Ollama that, if successfully exploited, could allow a remote, unauthenticated attacker to leak its entire process

cPanel has released updates to address three vulnerabilities in cPanel and Web Host Manager (WHM) that could be exploited to achieve privilege escalation, code execution,

Threat hunters have flagged a previously undocumented Brazilian banking trojan dubbed TCLBANKER that’s capable of targeting 59 banking, fintech, and cryptocurrency platforms. The activity is

Cybersecurity researchers have discovered fraudulent apps on the official Google Play Store for Android that falsely claimed to offer access to call histories for any

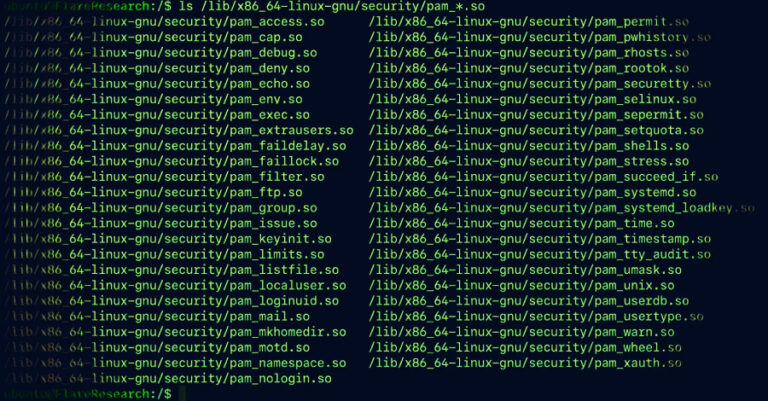
Cybersecurity researchers have disclosed details of a new Linux backdoor named PamDOORa that’s being advertised on the Rehub Russian cybercrime forum for $1,600 by a