Six New U-Boot Flaws Could Let Malicious Images Crash Devices or Run Code at Boot
Researchers at firmware security firm Binarly have found six new flaws in U-Boot, the small program that starts up hardware as varied as home routers, smart cameras,
Researchers at firmware security firm Binarly have found six new flaws in U-Boot, the small program that starts up hardware as varied as home routers, smart cameras,
Unknown threat actors compromised the Injective Labs SDK project’s GitHub repository and leveraged it to publish a malicious package on the npm registry to steal

Details have emerged about three now-patched security flaws in the OpenClaw personal artificial intelligence (AI) assistant that, if successfully exploited, could enable credential theft, privilege

Researchers at Ledger’s Donjon security team have shown that a precisely timed laser pulse, aimed at the chip inside a Tangem crypto wallet card, can reset the
The China-linked cybercrime group known as Silver Fox has been attributed to a new Rust-based remote access trojan (RAR) called MODBEACON. Chinese cybersecurity company QiAnXin

A threat actor has been targeting organizations spanning multiple sectors with voice-based fake security requests that prompt Microsoft 365 users to enroll a new Entra

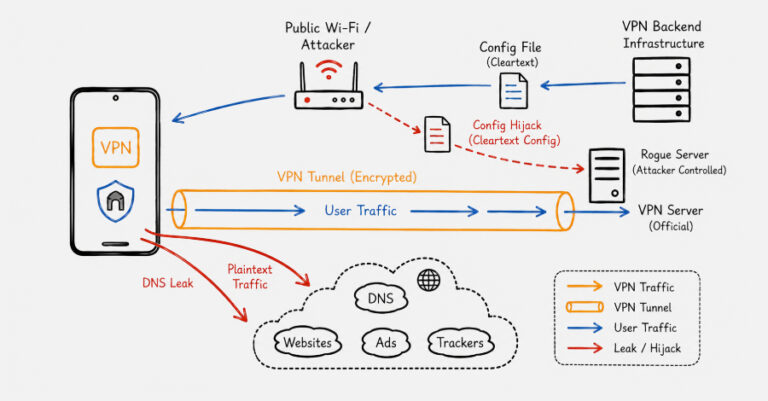
Researchers ran 281 of the most popular free VPN apps on the Google Play Store through a new testing system and found that many fail

A cybercrime crew left one of its own servers wide open on the internet for three weeks, and it exposed the operation’s inner workings: the

Most enterprises assume their asset inventory is close enough to accurate. The evidence suggests otherwise. According to a survey of over 600 security leaders in

A single wrong variable on one line in XQUIC, Alibaba’s QUIC and HTTP/3 library, lets any remote client crash the server with a short burst