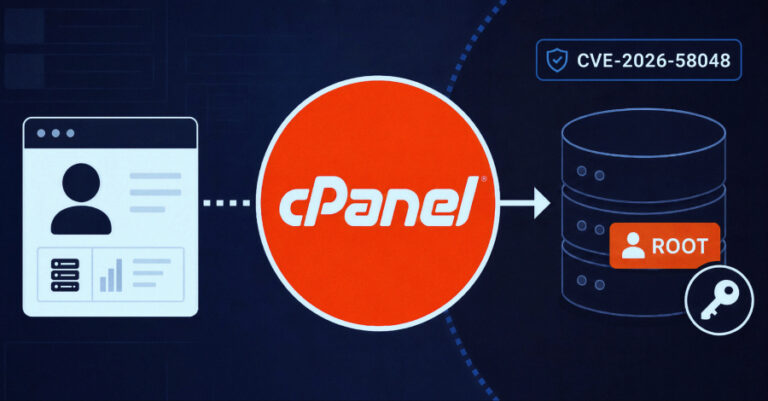
New cPanel Critical Flaw Could Let Hosting Customers Run SQL as Database Root
cPanel has patched a flaw that let an authenticated hosting customer execute SQL in the database’s root context, crossing the privilege boundary between a cPanel
cPanel has patched a flaw that let an authenticated hosting customer execute SQL in the database’s root context, crossing the privilege boundary between a cPanel
A new Russian loader-as-a-service (LaaS) codenamed DOUBLECUP has been using ClickFix lures as a way to stage malware-laced PNG images in victims’ browser cache and

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a high-severity security flaw impacting N-able N-central to its Known Exploited Vulnerabilities (KEV) catalog

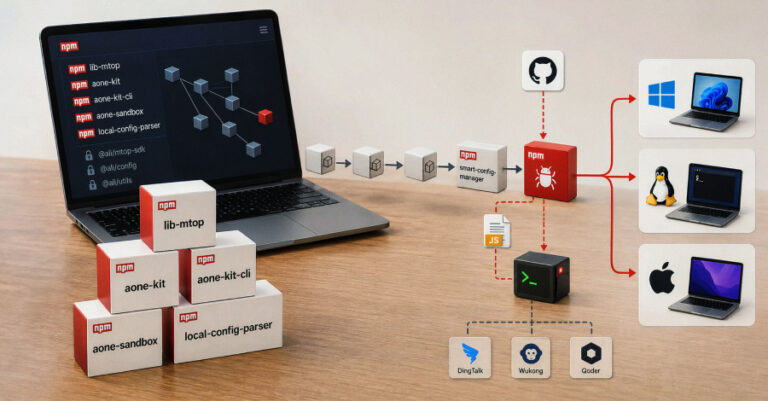
Cybersecurity researchers have discovered a new set of malicious npm packages that target users of Alibaba developer tools with a cross-platform remote access trojan (RAT)

The INC Ransomware operation has emerged as the “dominant threat actor” exploiting the recently disclosed security flaws in SonicWall Secure Mobile Access (SMA) 1000 series

Malware running as an ordinary user on a Windows machine can sign into a victim’s passkey-protected accounts without a fingerprint, a PIN, or anything at

This week kept coming back to permission. A model crossed a boundary. A wallet trusted bad randomness. Webmail kept an intruder around. Public systems, package

AI is moving incredibly fast, and every security leader is feeling the pressure to keep up. AI platforms like Claude, Codex and Cursor are already

The Police National Legal Database (PNLD) has confirmed that police, government and customer contact information was compromised and published on the dark web. The data

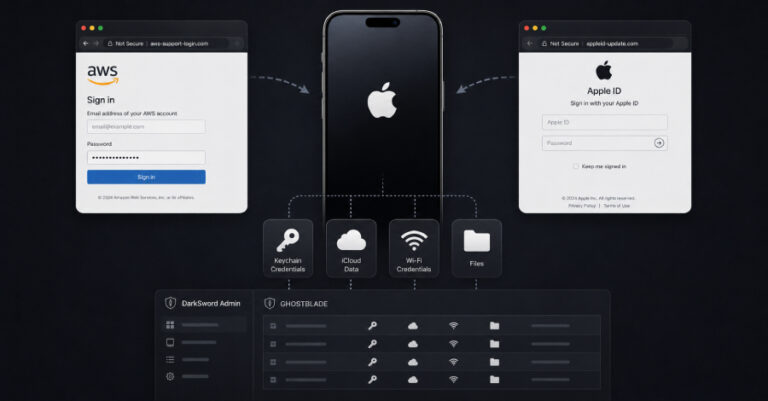
An unknown Chinese-threat actor has been observed running a campaign targeting Apple iOS devices by leveraging a publicly leaked version of the DarkSword exploit kit.