Industry News
New OVSwrap Linux Kernel Flaw Lets Local Users Gain Root via Open vSwitch
A memory corruption flaw in the Linux kernel’s Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured
A memory corruption flaw in the Linux kernel’s Open vSwitch datapath gives ordinary local users a path to root on a broad set of default-configured
A cluster of 77 extensions on the Open VSX marketplace has been found to impersonate legitimate developer tools while transmitting information about the systems and
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on August 5, 2026, added three flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of
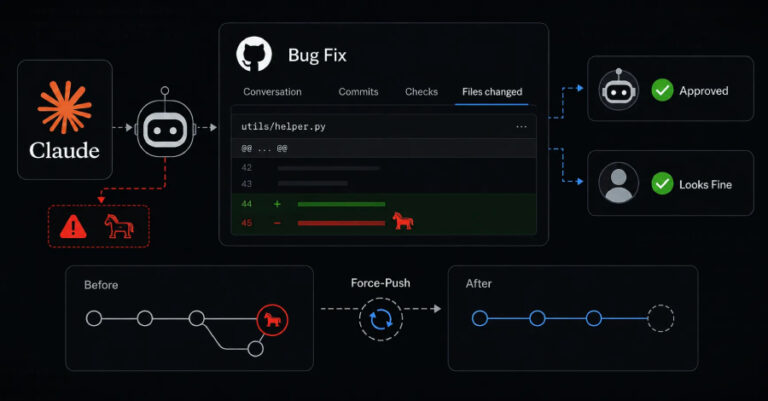
An agent running Anthropic’s Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project during a cyber
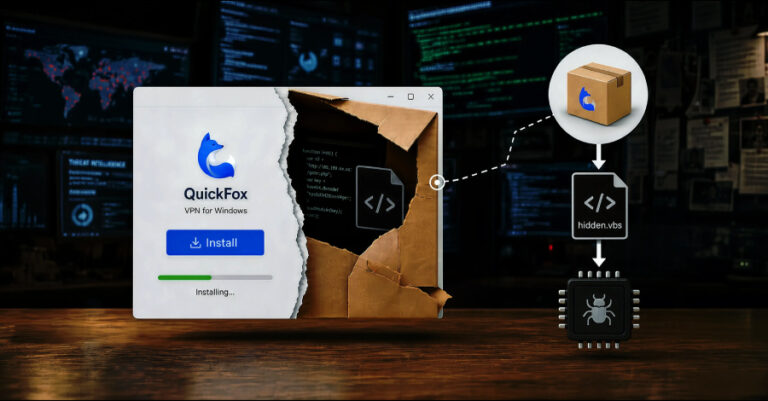
Cybersecurity researchers have disclosed what has been described as a “long-standing supply chain attack” on QuickFox, a virtual private network (VPN) and network acceleration tool
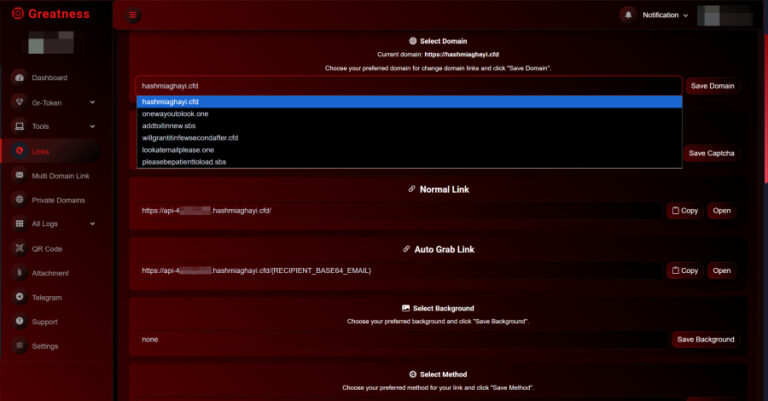
The commercial phishing-as-a-service (PhaaS) toolkit known as Greatness has become the latest crimeware solution to add support for device code phishing, a rapidly growing cyber
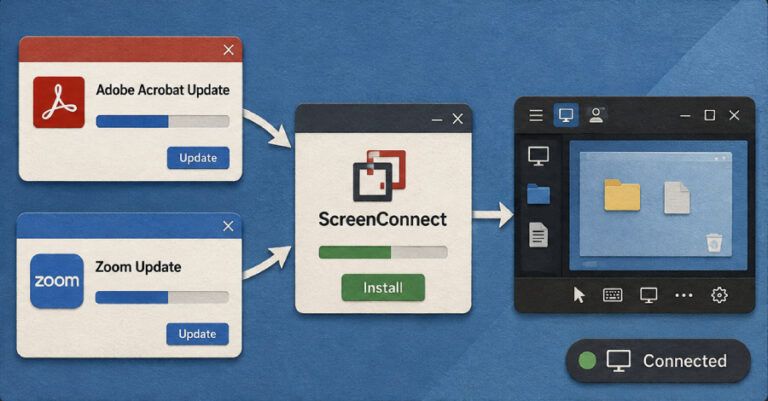
Cybersecurity researchers have disclosed details of an active, multi-wave campaign that employs social engineering lures themed around Adobe and Zoom software updates, business document reviews,
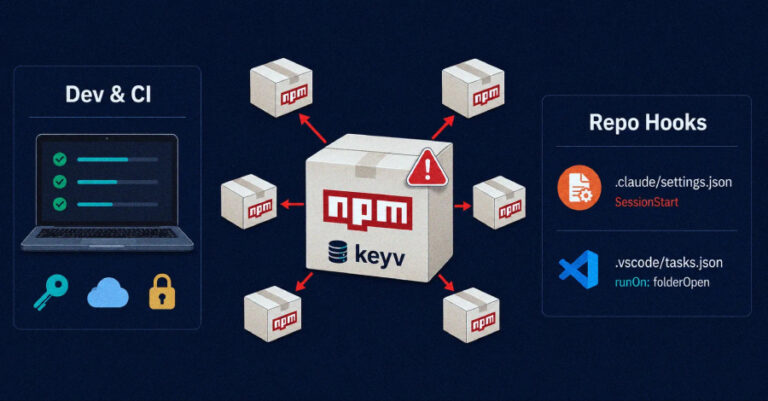
A credential-stealing npm worm that first appeared in keyv@6.0.0 spread beyond the Keyv and Cacheable namespaces into hundreds of packages across multiple organizations on August
Google deleted three AI agent workflows from its Agent Development Kit (ADK) Python repository. Pillar Security showed that a public GitHub issue could manipulate a
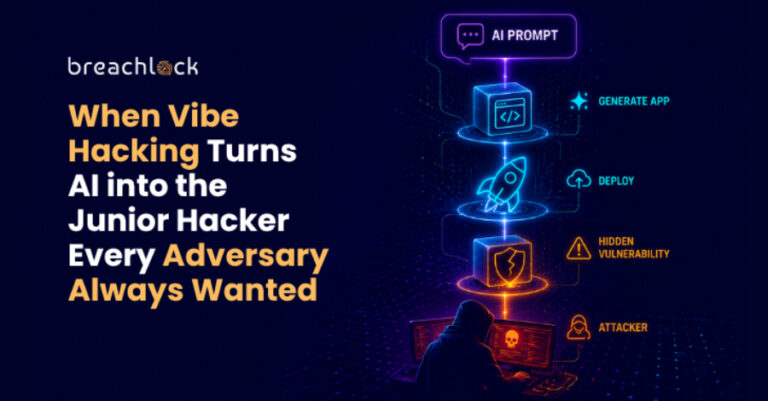
The cybersecurity industry has spent decades assuming that offensive capability scales with technical expertise. That assumption is starting to break. Security teams have long estimated