Fake Web3 Accelerator Uses npm Packages to Spread Malware and Hijack AI Agent Traffic
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of
An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users

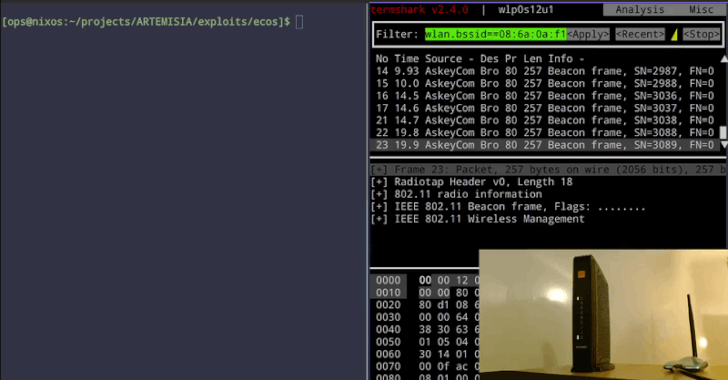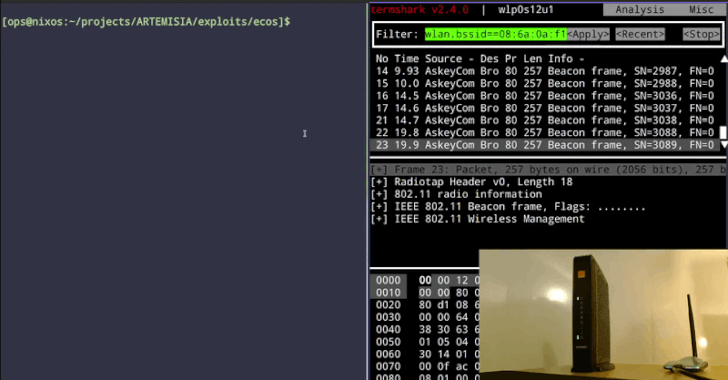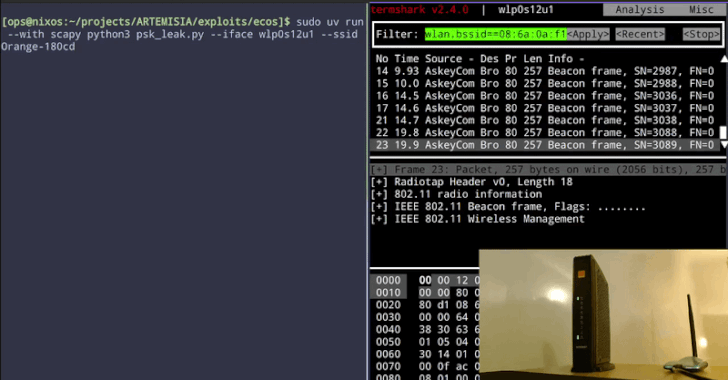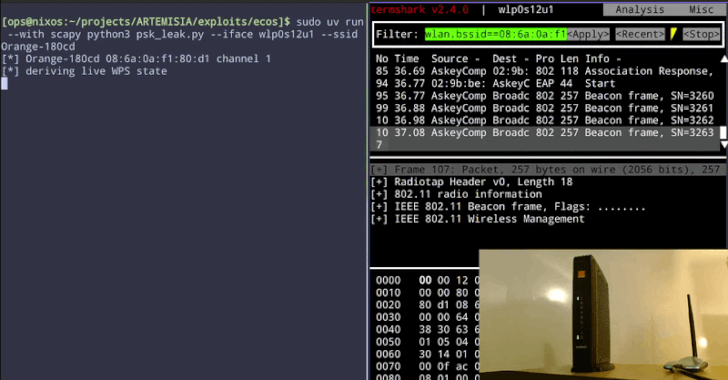
A flaw in Broadcom’s Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or

ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained

Cybersecurity researchers have discovered a malicious npm package that’s part of a recently disclosed software supply chain attack campaign dubbed MALFEX. The package, named “imgdecode,”

Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging

Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor’s own update servers, in windows of five to ten minutes at a time

A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims

OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not