Industry News
From Email-to-Case to the Boardroom: How Inherited Agents Break Governance Built for Software
In Salesforce Agentforce, the recommended way to make an agent respond to events is a Flow: a record is created or a case is updated,

In Salesforce Agentforce, the recommended way to make an agent respond to events is a Flow: a record is created or a case is updated,
The threat actor behind the GhostAction supply chain attack has expanded beyond injecting malicious GitHub Actions workflows into compromised projects to phish open-source developers and
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of
An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users
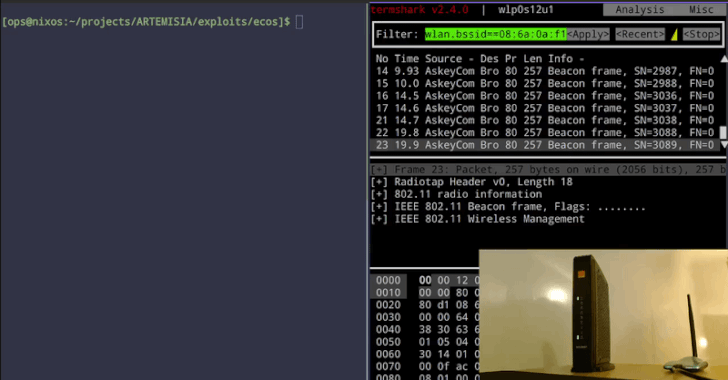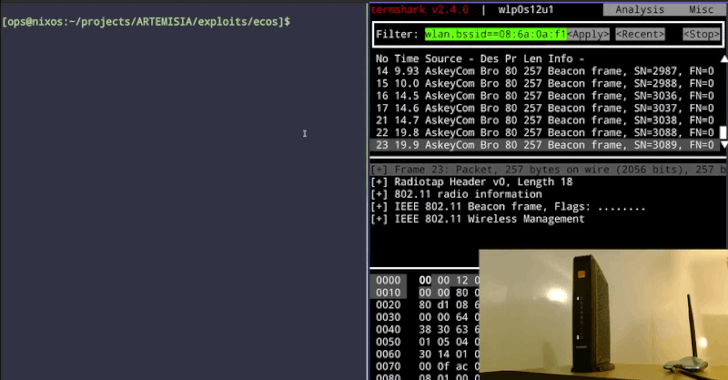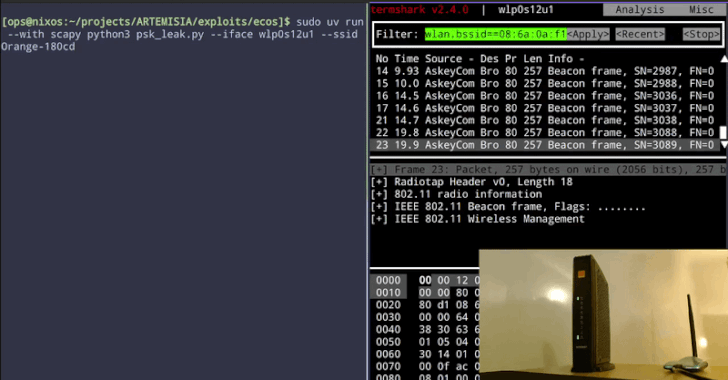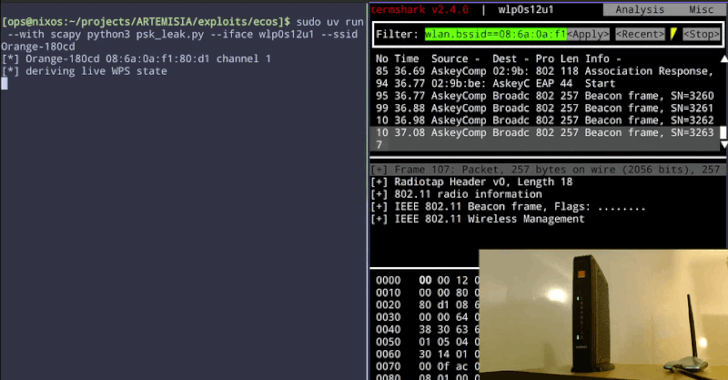
A flaw in Broadcom’s Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or
ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained
Cybersecurity researchers have discovered a malicious npm package that’s part of a recently disclosed software supply chain attack campaign dubbed MALFEX. The package, named “imgdecode,”
Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor’s own update servers, in windows of five to ten minutes at a time
A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing