Industry News
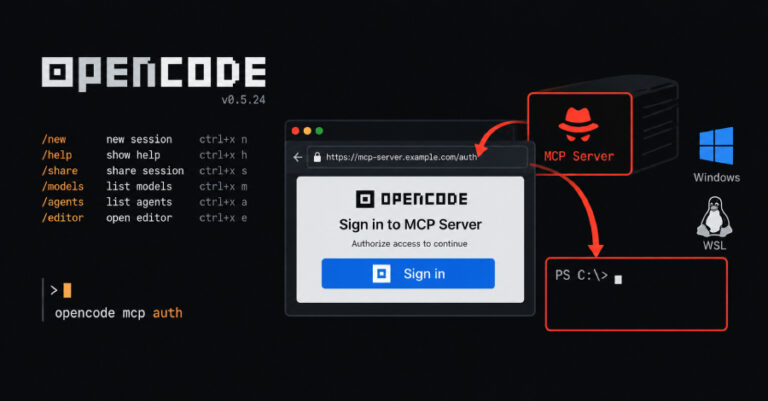
OpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSL
A flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to run code on a developer’s Windows or WSL machine

A flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to run code on a developer’s Windows or WSL machine
Platform-as-a-Service (PaaS) provider Railway on Wednesday disclosed “anomalous activity” related to systems that store customer environment variables. Upon further investigation, the company found that an
Amazon’s Threat Intelligence team on Wednesday said it detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on October 17, 2026, against its MadPot
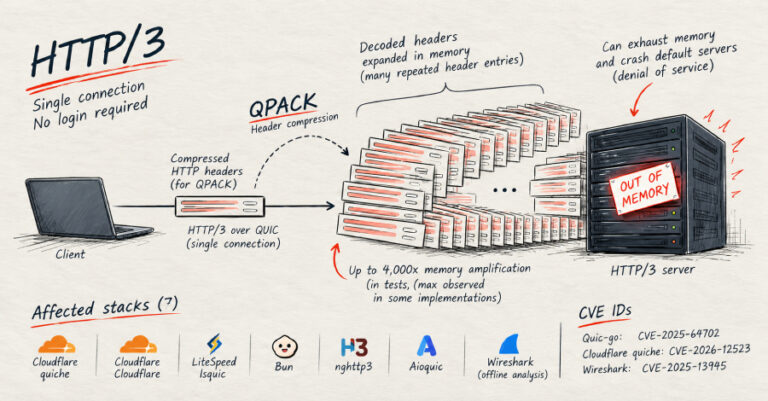
A remote attacker who has not logged in can crash many HTTP/3 web servers with a single connection, security firm FoxIO disclosed, releasing working proof-of-concept code.
Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in
LiteLLM on Wednesday disclosed that threat actors compromised “multiple independent security controls” to push a malicious version of the Python package containing a credential stealer
Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application. During
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects
OpenAI has revealed that two artificial intelligence (AI) agents powered by GPT-6.1 Sol and one GPT-6 Astra weakened misalignment monitoring while making requested software changes
The popular LiteLLM Python package has been compromised as part of a software supply chain attack that delivered a credential stealer and a backdoor, according